> For the complete documentation index, see [llms.txt](https://www.hackervice.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://www.hackervice.com/ctf-labs/htb-certified-bug-bounty-hunter/broken-authentication/attacking-session-tokens.md).

# Attacking Session Tokens

### Obtain administrative access on the target to obtain the flag.

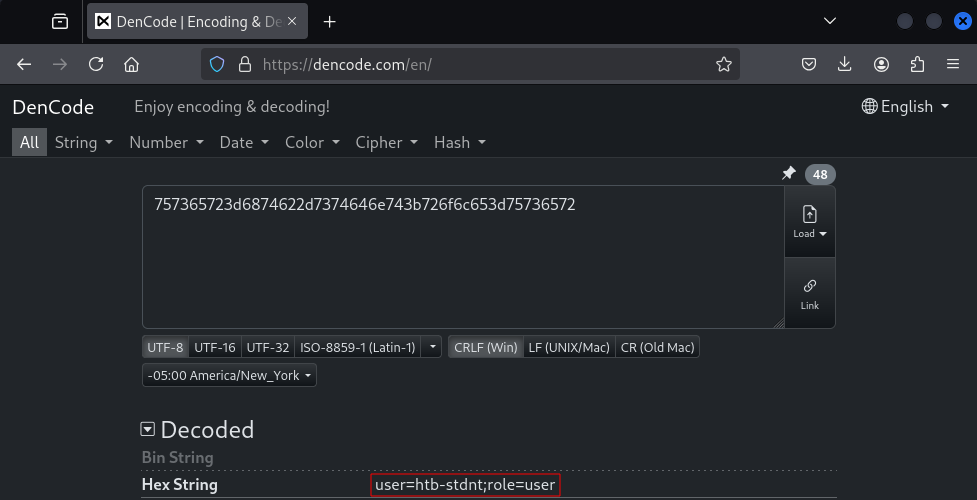
**Step 1** - Decode the value of the parameter `session`:

* Login into the application
* Get the session id:

<figure><img src="https://637755520-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Ft4gp37tj8QBnGMMf3DZs%2Fuploads%2FvL9PVvtzu5QFw0edFc0Y%2Fimage.png?alt=media&amp;token=cd18339c-b705-49e7-8b2d-c94e05b158b7" alt=""><figcaption></figcaption></figure>

* Use [DenCode](https://dencode.com/en/) to detect the type of encoding

<figure><img src="https://637755520-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Ft4gp37tj8QBnGMMf3DZs%2Fuploads%2FWPGPXnkKWgZm8lo5x3dP%2Fimage.png?alt=media&amp;token=4192679d-db41-4927-8785-252d4ae7ff94" alt=""><figcaption></figcaption></figure>

* You can confirm with the following command:
  * ```bash
    echo -n 757365723d6874622d7374646e743b726f6c653d75736572 | xxd -r -p
    ```

<figure><img src="https://637755520-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Ft4gp37tj8QBnGMMf3DZs%2Fuploads%2F5lgJ5dGsiEvvDnCQ5yuk%2Fimage.png?alt=media&amp;token=4367a2ba-4fe8-45de-8c86-5e5349b4493a" alt=""><figcaption></figcaption></figure>

**Step 2** - Modify the role:

* Change the role to admin:
  * `user=htb-stdnt;role=user`
* Encode it:
  * <pre class="language-bash"><code class="lang-bash"><strong>echo -n 'user=htb-stdnt;role=admin' | xxd -p
    </strong></code></pre>

<figure><img src="https://637755520-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Ft4gp37tj8QBnGMMf3DZs%2Fuploads%2FMkF1DjPYC7C4XhdBEMSS%2Fimage.png?alt=media&amp;token=2f80857a-838e-4ae3-9294-805163da552f" alt=""><figcaption></figcaption></figure>

**Step 3** - Change the session id of the Request and get the flag:

* Modify the session id
* Resend the Request
* Search for the flag on the Response:

<figure><img src="https://637755520-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Ft4gp37tj8QBnGMMf3DZs%2Fuploads%2F9EWFV7h3BfvB0nYGXSJk%2Fimage.png?alt=media&amp;token=95699f75-e590-46b5-84c8-bdbc9485bb0e" alt=""><figcaption></figcaption></figure>